About Us
We built what we wanted to deploy ourselves.
Arrakis Security was founded to solve the governance problem that emerges when enterprises start deploying autonomous AI agents at scale.
Why We Exist
The problem gets harder as the fleet grows.
AI agents are different from the software systems enterprises have managed before. They do not follow deterministic code paths. They can follow chains of tool calls and API requests that their designers did not anticipate. A single agent with a broad mandate and no explicit boundaries is a liability waiting to materialize.
Managing one agent is tractable. Managing 50 or 200, across multiple departments, each with different permission requirements and different risk profiles, is not tractable without purpose-built infrastructure. That is the gap Arrakis fills.
We believe the enterprises that will benefit most from autonomous AI will be the ones that build governance into their agent deployments from the start -- not as an afterthought, but as a structural property of how their agents are deployed.
2025
Founded
Austin, TX
Headquarters
Enterprise security
Focus
Independently funded
Stage
The Team
The people building Arrakis.
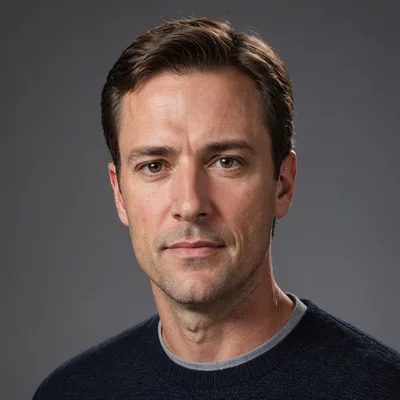
Marcus Webb
CEO and Co-Founder
Spent several years building detection infrastructure and access-control systems for a cloud security tooling company before co-founding Arrakis. He saw the permission boundary problem emerging in early enterprise AI deployments and became convinced it needed a dedicated solution.
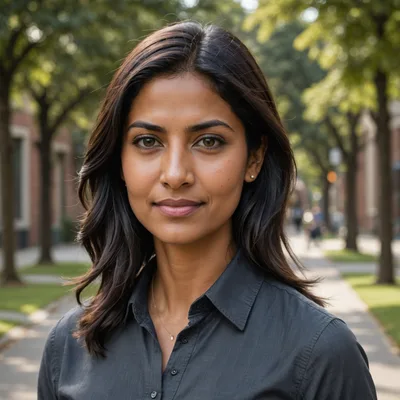
Priya Nair
CTO and Co-Founder
Led distributed policy-enforcement systems and runtime security for containerized environments before co-founding Arrakis. Her background is in systems that need to enforce access rules at high throughput without becoming a bottleneck. She designed the core policy engine.
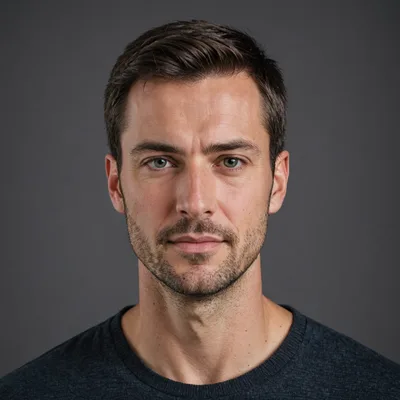
Dmitri Volkov
Head of Engineering
Built real-time event streaming and anomaly detection pipelines at a large-scale data infrastructure company before joining Arrakis. He leads the team building the Arrakis console, the instrumentation SDKs, and the data pipeline that powers the audit trail.
We are a small team. If you are interested in working on the AI governance problem with us, reach out through the contact page.
Get in TouchValues
How we work.
Solve the actual problem
We ask "what does the enterprise actually need to feel safe deploying AI agents" before asking "what is technically interesting to build". The answers sometimes overlap. When they do not, the first question wins.
Honest about limitations
Arrakis is not a complete AI safety solution. It is a permission boundary enforcement and audit tool. We say that plainly. Overstating what a security tool does is how enterprises get false confidence and then get burned.
Build for the operator
The people who use Arrakis are security engineers, platform engineers, and compliance managers. The tool should be clear to them, not optimized for demos. If a dashboard is confusing to a security analyst at 2am, it needs to be redesigned.
Build deliberately
We add capabilities when they are needed by customers, not when they make good press release copy. A small surface area is a virtue in a security product. Every feature is something we need to secure and maintain forever.
Want to learn more?
We talk with security and platform engineers at enterprises deploying AI agents. No pitch decks unless you want one.